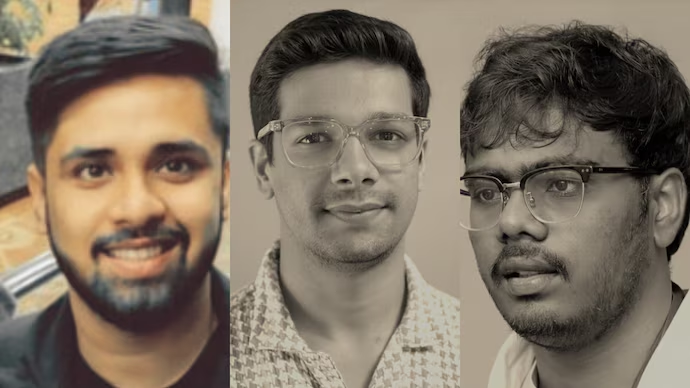
Three Indian-origin cybersecurity researchers have demonstrated how artificial intelligence can accelerate sophisticated security testing after using Anthropic’s Claude to exploit vulnerabilities in OpenAI’s systems.
The researchers — Harsh Jaiswal, Mohan Pedhapati and Rahul Maini — are associated with cybersecurity startup Hacktron AI. Their work was conducted as part of authorised security research under OpenAI’s bug-bounty programme, rather than a conventional malicious attack.
According to reports and the researchers’ account, the team discovered a vulnerability in OpenAI’s community forum and used Claude to help develop and execute parts of the exploit chain. The researchers eventually demonstrated access to multiple OpenAI employee ChatGPT and Codex accounts and established a route into the company’s private GitHub environment.
The research reportedly took less than 72 hours from the initial discovery to demonstrating access to OpenAI’s internal repository. The team spent less than $3,000 on AI tokens during the broader effort, according to reports. OpenAI subsequently paid the researchers a $6,500 bug bounty after the vulnerabilities were disclosed.
The investigation began with OpenAI’s community forum, which runs on the third-party Discourse platform. Researchers identified a vulnerability involving the processing of specially crafted HEIF image files. The flaw was connected to the libheif image-processing library and could be exploited to achieve remote code execution.
From there, the researchers were able to move through an authentication-related weakness and obtain access linked to OpenAI employee accounts. This created a path from the public-facing forum environment to internal services.
Rather than accessing or downloading sensitive proprietary material, the researchers said they stopped after establishing that the route worked. To demonstrate their access, they used a compromised employee’s Codex account to create a harmless pull request in OpenAI’s private repository.
The episode has drawn attention because of the role played by Claude in the research. The researchers used Anthropic’s AI tools to assist with analysing the vulnerability, generating code and accelerating parts of the exploit-development process. Their findings illustrate how increasingly capable AI systems can reduce the time and resources needed for complex cybersecurity research.
OpenAI fixed the vulnerabilities after receiving the researchers’ disclosures and revoked affected authentication tokens and sessions, according to reports. The company also thanked the researchers for reporting the issues.
The incident has added to a growing discussion within the technology industry over AI-assisted cybersecurity. While AI tools can help defenders identify and patch vulnerabilities faster, the same capabilities can also help researchers — and potentially malicious actors — automate parts of sophisticated cyber operations.
For Jaiswal, Pedhapati and Maini, the OpenAI research ultimately became a demonstration of how AI can change the speed and scale of vulnerability discovery, while also highlighting the importance of strong authentication controls and careful security boundaries around connected AI systems.